Governance, Risk, and Compliance (GRC) programs have become increasingly complex in modern enterprises. Organizations face expanding regulatory requirements, evolving cybersecurity threats, and resource constraints while trying to build and maintain effective compliance programs. This complexity has led to the emergence of Managed Assurance, often defined as compliance-as-a-service, a structured approach to Governance, Risk, and Compliance.
Managed Assurance is more than a buzzword, it’s a practical solution for modern compliance challenges. For readers who want a foundational overview, our article “What Is Managed Assurance?” explains the concept and why it matters for organizations navigating complex regulatory landscapes.
Understanding Managed Assurance
Managed Assurance represents a comprehensive approach to GRC that combines dedicated expertise with systematic processes. This model addresses common challenges in traditional GRC implementations, including regulatory alignment, scalability limitations, and resource allocation.
Through continuous monitoring, proactive auditing, and systematic reporting, Managed Assurance transforms GRC from a reactive compliance exercise into an integrated part of business operations. This approach helps organizations maintain consistent compliance while supporting strategic growth.
Proactive Risk Management
Managed Assurance incorporates real-time monitoring to identify potential compliance issues before they impact operations. This approach helps organizations protect their financial, reputational, and operational stability through early detection and mitigation of risks.
Resource Optimization
Compared to maintaining comprehensive in-house GRC teams, Managed Assurance provides more predictable cost structures. Organizations can access specialized expertise and tools without significant infrastructure and workforce investments.
Scalable Implementation
As organizations grow and enter new markets, their GRC requirements typically become more complex. Managed Assurance frameworks are designed to adapt to changing compliance needs across different jurisdictions and regulatory environments.
Automated Compliance Management
Automated tracking and reporting systems streamline audit preparation and documentation processes. This automation enables organizations to maintain accurate compliance records while reducing manual oversight requirements.
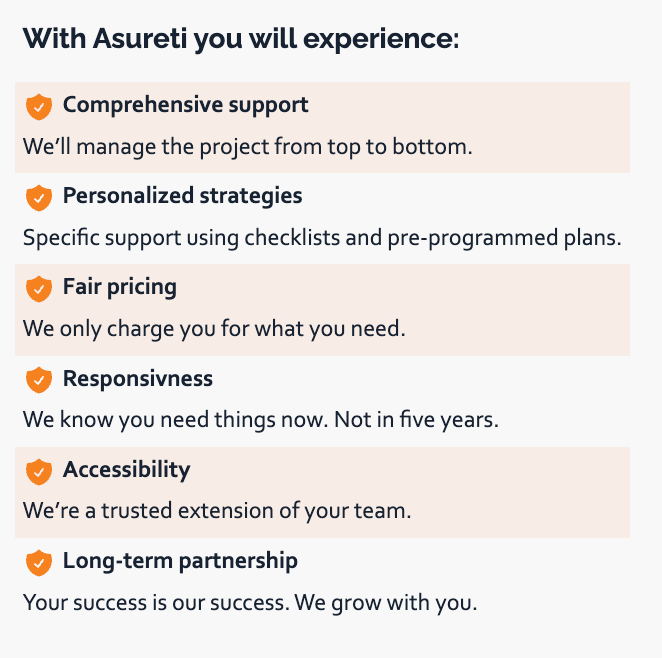
Operational Benefits
Continuous Monitoring
Real-time oversight provides visibility into compliance status across the organization. This continuous monitoring helps maintain consistent standards and enables prompt response to emerging issues.
Centralized Management
Unified platform for audit management, policy administration, and regulatory tracking reduce complexity and improve visibility. This centralization helps organizations maintain consistent compliance standards across operations.
Data-Based Decision Support
Systematic collection and analysis of compliance data support evidence-based decision-making for risk management and strategic planning.
Evaluating Managed Assurance Providers
When selecting a Managed Assurance partner, organizations should consider:
- Industry-specific compliance expertise
- Flexibility in use of technology and tooling
- Implementation experience in similar environments
- Integration capabilities with existing systems
- Familiarity with varied obligations, frameworks, and third-party requirements
Staying informed about evolving risk and compliance trends is essential. Risk Management Magazine offers a wide range of articles on enterprise risk, regulatory changes, and governance strategies. Reviewing their insights can help you better understand the broader context of GRC challenges and make more informed decisions when selecting a Managed Assurance partner.
If you’re looking for a deeper perspective on how this model works in practice, the Managed Assurance White Paper offers detailed insights into frameworks, scalability, and operational benefits that help organizations stay ahead of risk.
Implementation Considerations
Organizations considering Managed Assurance should evaluate their current GRC processes, compliance requirements, and resource allocation. This assessment helps determine the appropriate scope and scale of managed services needed.
Successful implementation typically requires:
- Clear definition of compliance requirements
- Assessment of current GRC processes
- Identification of integration points within existing systems
- Development of transition and training plans
- Clear and focused attention on change management
Technology decisions can make or break a compliance program. Our GRC Platform Selection Case Study shows how companies choose tools that support growth without adding unnecessary complexity.
Conclusion
Managed Assurance offers organizations a structured approach to managing increasingly complex GRC requirements. By combining specialized expertise with systematic processes and technology, this model helps organizations maintain effective compliance programs while optimizing resource utilization.
For more information about implementing Managed Assurance in your organization, read our Managed Assurance case study.
FAQ
What exactly is “Managed Assurance,” and how does it differ from traditional Governance, Risk, and Compliance (GRC) consulting or point-in-time assessments?
Managed Assurance (aka Compliance-as-a-service) is Asureti’s ongoing compliance and risk management service that replaces one-time assessments and traditional Governance, Risk, and Compliance (GRC) consulting with a continuous, embedded program. Instead of hiring consultants for short-term fixes or scrambling for audits, Managed Assurance gives you a dedicated team that builds and runs your GRC program day-to-day. It’s designed to help you efficiently managed a program aligned frameworks like SOC2, PCI, HIPAA, HITRUST, ISO, NIST, CMMC, and more without overwhelming your internal resources. You get proven workflows, ready-to-use GRC technology, training and support, and strategic oversight that evolve with your business. Compliance becomes predictable, audits are smoother, and your team can focus on growth instead of firefighting.
Who is Managed Assurance designed for?
Managed Assurance is built for lean teams, growing companies, and regulated industries that need expert compliance support without hiring a full internal GRC staff. Many organizations struggle to keep up with audits, certifications, and evolving regulations, especially in sectors like healthcare, AEC, Fintech, manufacturing, SaaS/tech, and insurance. Asureti’s solution embeds a trusted team, proven workflows, and scalable technology directly into your operations. Whether you’re preparing for your first certification or trying to mature your risk program, Managed Assurance helps you stay ahead without burnout. The result is predictable compliance, stronger stakeholder trust, and readiness for growth, funding, or M&A.
What does Asureti’s Managed Assurance include?
Managed Assurance includes everything needed to run a full compliance and risk program without building it from scratch internally. Many organizations struggle with fragmented audits, unclear policies, and limited bandwidth. Asureti solves this by providing a dedicated team, proven workflows, process accelerators and content, and GRC technology that covers risk assessments, privacy and vendor reviews, policy and control management, audit prep and audit defense, findings management, and regulatory alignment. You also get integrated reporting, process accelerators, and strategic advisory support. The result is a scalable, repeatable program that reduces operational risk, simplifies compliance, and builds trust with clients and regulators.
How does Managed Assurance help with audits and certifications?
Managed Assurance helps with audits and certifications by acting as your audit prep partner and audit defense team. Instead of scrambling before deadlines, Asureti builds and manages your internal controls, organizes audit evidence, and supports you during client inquiries, regulator visits, and in-person audits. The service includes readiness assessments, policy drafting, control testing, and continuous monitoring, all aligned to frameworks like SOC2, HITRUST, ISO, and CMMC. The result is fewer exceptions, faster certifications, and confidence that your organization is prepared.
What is Asureti’s Managed Assurance fee model—what does that include, and how predictable is it for budgeting?
Budgeting for compliance is sometime unpredictable, with hidden costs tied to audits, consultants, unexpected changes, and internal staffing gaps. Asureti’s Managed Assurance solves this with a fixed monthly fee that covers everything needed to run your GRC program, risk assessments, vendor reviews, control testing, audit cycles, policy management, continuous monitoring, and ongoing advisory support. You get a dedicated team, proven workflows, and access to ready-to-use GRC technology without needing to hire or train internally. The result is predictable budgeting, reduced operational risk, and a scalable compliance program that quickly grows with your business.
Can Managed Assurance scale as our regulatory and compliance needs evolve?
As organizations grow, their compliance needs often become more complex and harder to manage – and with higher risks of failure. Asureti’s Managed Assurance is built to scale with you. It adapts to new regulations, business lines, and risk profiles by offering flexible workflows, customizable components, and a team that adjusts as your priorities shift. Whether you’re expanding into new markets, facing new audit requirements, acquiring new entities, or integrating additional systems, the service evolves with your business. The result is an adaptable and prepared compliance program that supports growth, reduces risk, and keeps you ahead of regulatory change without needing to rebuild your GRC foundation.
Do you have case studies showing quantifiable results?
Many organizations face audit fatigue, missed deadlines, and compliance gaps due to limited internal resources and lack of GRC expertise. Asureti’s Managed Assurance has helped clients overcome these challenges by embedding a full compliance program that includes control testing, policy management, and audit prep. In one case study, a SaaS platform company reduced SOC2 report exceptions by 80%, completed annual testing of 182 controls, and implemented a successful Type 1 and Type 2 SOC program in just nine months, all without hiring additional staff. The result was retained client contracts, streamlined audits, and a scalable GRC foundation that supported future growth. In our client’s words: “Asureti empowered us to gain our HITRUST certification in just eight months. Through their tailored Managed Assurance program, we were able to put our HITRUST, HIPAA and annual testing requirements pretty much on auto-pilot. They helped us to an in-depth discovery and tailored their approach to our needs.” You can read more about our case studies here.
How do we get started—what does the discovery process or initial engagement look like?
Getting started with Asureti’s Managed Assurance begins with a focused discovery session where we align on your compliance goals, current environment and requirements, and operational constraints. This initial engagement is designed to be efficient and strategic. Asureti gathers key documentation, maps out your regulatory landscape (SOC2, HIPAA, CMMC, HITRUST, etc.), and identifies gaps that could impact client trust or audit readiness. From there, we define a tailored roadmap that prioritizes what matters most to your stakeholders and builds toward continuous assurance without adding unnecessary overhead. Get started now!
Justin Zambo
For more than 25 years, Justin has turned complex privacy, GRC, and security challenges into simple solutions. He works with Asureti’s clients to protect their data. Frameworks include ISO, SOC 2, HITRUST, HIPAA, NIST, CMMC, and GDPR. His work also covers AI governance and state privacy laws. He loves building strategies that hit ambitious goals and open new markets. His small-town Kansas roots taught him grit and hard work. His motto says it all: "Go Get'em!"